One Country, Fifty Rulebooks: How Fragmented State Privacy Laws Are Forcing Enterprises to Over-Engineer Their Infrastructure
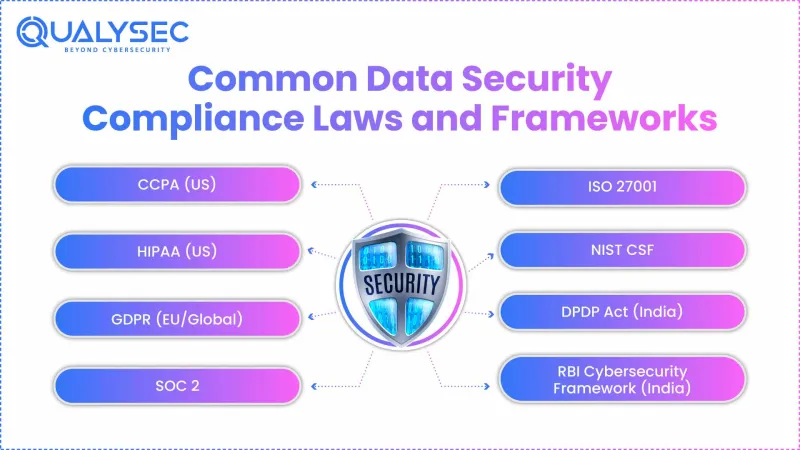
Photo: data compliance enterprise server infrastructure legal documents, via qualysec.com
The Compliance Map No One Warned You About
When California's Consumer Privacy Act took effect in 2020, many enterprises treated it as a single obligation to address and move on. Four years later, the landscape looks nothing like that early assumption. Virginia, Colorado, Connecticut, Texas, Montana, and more than a dozen other states have since enacted their own data privacy statutes — each with distinct definitions of personal data, varying opt-out mechanisms, and inconsistent enforcement timelines.
For enterprises operating across multiple states, the cumulative effect is not additive. It is exponential. A healthcare organization headquartered in Texas, serving patients in California, processing billing data in a shared cloud environment, and employing remote workers in New York faces a matrix of overlapping obligations that no single compliance framework was designed to manage.
This is the data residency maze. And the companies trapped inside it are spending real money — often unnecessarily — trying to find their way out.
When Regulations Pull in Opposite Directions
The core challenge is not that each regulation is individually complex. Most compliance officers can navigate a single framework with the right legal and technical support. The problem emerges at the intersections.
Consider the tension between HIPAA's minimum necessary standard — which limits data collection and retention to what is strictly required for a defined purpose — and certain state-level consumer privacy laws that require businesses to provide data portability, meaning they must retain enough structured information to fulfill export requests. In practice, a healthcare platform might be legally required to minimize retention under federal law while simultaneously obligated to maintain accessible, exportable records under state law.
Similarly, financial institutions subject to the Gramm-Leach-Bliley Act must contend with state-level amendments that impose stricter breach notification windows, different definitions of covered data, and in some cases, residency requirements that prohibit certain categories of data from being processed outside state borders.
"We spent eighteen months building a compliant data architecture for CCPA," said one compliance director at a mid-sized SaaS company based in the Pacific Northwest, speaking on background. "Then we expanded into Virginia and realized our tagging logic didn't map to their consent model. We had to go back and re-instrument a significant portion of our pipeline."
The Infrastructure Response: Silos as a Coping Mechanism
Faced with regulatory ambiguity, many enterprise IT teams have defaulted to a familiar but costly solution: geographic and logical data silos. The reasoning is straightforward — if data for California residents lives in a California-compliant environment, and data for Texas residents lives in a separate stack, enforcement risk is contained.
The problem is that this approach scales poorly and introduces new categories of operational risk. Duplicate infrastructure means duplicate maintenance costs, duplicate security surfaces, and duplicate failure points. Data that should inform a unified analytics model becomes fragmented across jurisdictions, degrading the quality of business intelligence. Integration projects that once required weeks now require months of compliance review.
IT architects at enterprises that have gone down this path describe a kind of compliance debt — structural decisions made under regulatory pressure that accumulate technical and financial costs over time.
Smarter Strategies for Compliant Architecture
The enterprises navigating this space most effectively are not the ones with the largest compliance teams. They are the ones that made deliberate infrastructure investments early, before the regulatory environment became this complex.
Several practical approaches have emerged as industry best practice:
Data classification at ingestion. Rather than categorizing data retroactively, leading organizations are building classification logic directly into their ingestion pipelines. Every record is tagged at the point of entry with jurisdiction flags, sensitivity categories, and applicable regulatory frameworks. This allows downstream systems to apply the correct controls automatically, without manual intervention.
Policy-as-code frameworks. Instead of relying on documentation and manual review processes, compliance requirements are encoded directly into infrastructure-as-code templates. When a new state law takes effect, the policy update propagates through the environment systematically, rather than requiring individual teams to interpret and implement changes independently.
Unified consent management platforms. Rather than managing consent models separately for each jurisdiction, forward-thinking enterprises are deploying centralized consent infrastructure that can apply the most restrictive applicable rule across a user's entire data profile. This approach may slightly over-comply in some jurisdictions, but it dramatically reduces operational complexity and legal exposure.
Federated data governance models. Some organizations are adopting governance structures in which a central team sets policy and tooling standards, but individual business units retain responsibility for compliance within their domain. This distributes the compliance burden without fragmenting the underlying architecture.
The Cost of Getting It Wrong
The financial stakes are not abstract. California's Attorney General has demonstrated a willingness to pursue enforcement actions against enterprises that fail to honor opt-out requests or maintain adequate data security practices. The Texas Data Privacy and Security Act, which took effect in 2024, allows the state's Attorney General to seek civil penalties of up to $7,500 per violation. For a large enterprise processing millions of consumer records, the exposure is significant.
Beyond direct penalties, the reputational cost of a high-profile compliance failure can be substantial. In an environment where enterprise procurement increasingly involves vendor security and privacy assessments, a documented compliance gap can disqualify a company from contracts it would otherwise win.
Building for the Regulatory Future
The trajectory of US data privacy law is not toward simplification. More states will enact their own statutes. Federal privacy legislation, if and when it passes, will likely coexist with rather than preempt state frameworks. Sector-specific regulations — in healthcare, finance, education, and telecommunications — will continue to evolve independently.
For enterprise IT and compliance leaders, the strategic imperative is clear: infrastructure decisions made today must be evaluated not only against current requirements but against the regulatory environment that is plausible two to five years from now. That means investing in adaptable architectures, not point solutions. It means treating compliance infrastructure as a strategic capability, not an overhead cost.
The enterprises that will navigate this landscape most effectively are those that stop treating data residency as a legal problem and start treating it as an engineering discipline.